From Annual Audits to Continuous Intelligence
Annual audits go stale in weeks. The agent monitors every vendor continuously, flagging risk signals within hours.
Procurement & Supply Chain
89% of enterprises had a supplier risk event in 2022–2023; 60% have no visibility beyond Tier 1 (Gartner). Disruptions cost $184M on average (IBM Resilinc).
Annual audits are inadequate — a supplier can pass in January, receive a sanctions designation in March, and fail a cyber audit in April.
$184M Book a vendor risk audit to map your single-source exposure and quantify your savings.
Business impact
89%
of enterprises experienced a supplier risk event in 2022–2023 — yet most had no early-warning system in place
Source: Gartner
Six capability pillars for proactive supplier risk management across procurement and risk teams in regulated industries.
Live risk scoring across six dimensions — financial, compliance, cyber, geopolitical, operational, and ESG.
Automated screening against OFAC, EU, UN, UK, and FATF watchlists — re-screened within hours of any update.
Tracks PAYDEX, Altman Z-scores, credit ratings, and payment trends — flagging insolvency risk 60–90 days early.
BitSight and SecurityScorecard tracking flags score deterioration, leaked credentials, and dark web exposure.
Country risk scoring covers political stability, trade restrictions, tariffs, and export controls, updated live.
ESG scores track environmental violations, carbon intensity, labour practices, and governance events.
89% of enterprises hit a supplier risk event in 2022–2023, at $184M average cost. Annual audits miss what changes in between.
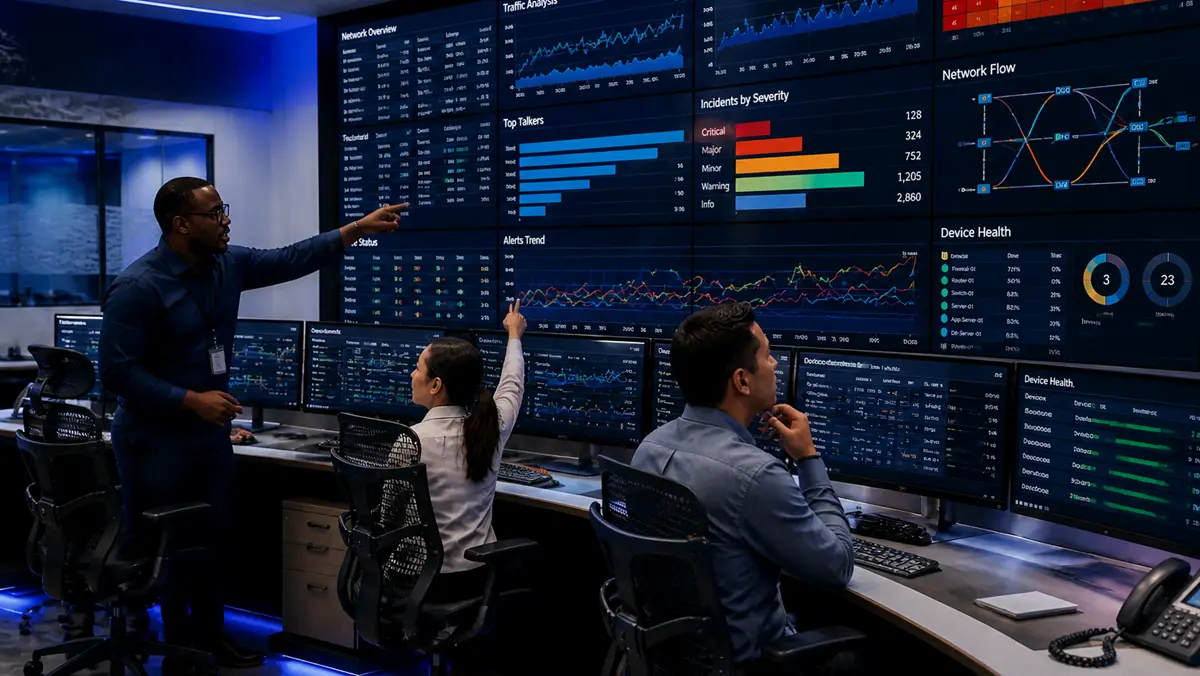
Annual audits go stale in weeks. The agent monitors every vendor continuously, flagging risk signals within hours.
60% of enterprises see nothing past Tier 1 (KPMG). The agent monitors sub-tier suppliers with the same intelligence.
Sanctions and FCPA breaches carry executive liability. Every screening decision keeps an inspection-ready audit trail.
Integrations
The agent connects to leading ERP, procurement, third-party risk data, and GRC platforms.
7 named systems it connects to
Running something not listed here? Tell us on the call — scoping the connector is the first step.
 AI Vendor Risk Monitor Agent
 SAP Ariba
 Oracle Fusion
 Coupa
SAP S/4HANA
 ServiceNow
 NetSuite
 Workday
Extract, classify and risk-score every clause in NDAs, MSAs and vendor contracts, so legal teams review faster with Bonami X AI's contract review…
View agentCategorise spend across every source with 95% accuracy, normalise supplier data and give procurement full spend visibility with Bonami X AI's spend…
View agentRetrieve approved answers, draft responses and assemble proposals so bid teams answer 70% of RFP questions automatically, with Bonami X AI's RFP…
View agentIt scores every vendor continuously across financial, sanctions, cyber, geopolitical, and ESG risk — detecting signals within hours, not at the next annual audit.
Six: financial (PAYDEX, Altman Z), sanctions (OFAC, EU, UN, FATF), cyber (BitSight, SecurityScorecard), geopolitical, operational concentration, and ESG.
It re-screens OFAC, EU, UN, UK, and FATF watchlists within hours of any update, covering UBOs, directors, and parent entities — not just the legal entity.
Insolvency signals surface 60–90 days early by combining PAYDEX trends, Altman Z-scores, credit downgrade watches, DPO changes, and news sentiment.
Yes, where sub-tier mapping data exists — Tier 1 from your ERP, sub-tier from Resilinc or D&B, all scored and alerted like direct vendors.
Critical alerts escalate immediately with automated PO suspension; high alerts route to the category manager on a 48-hour SLA, medium to a weekly digest.
Native integrations cover SAP Ariba, Oracle Fusion, Coupa, S/4HANA, ServiceNow TPRM, and MetricStream; custom ERPs connect via REST API and webhooks.
6–8 weeks: ERP integration and policy config, data validation, model calibration, then go-live — with first material alerts inside two weeks of launch.
Unlike traditional supplier risk management software, this vendor risk management software runs continuously — risks surface within hours, not at the next audit.
Yes. The TPRM software covers every active vendor and extends vendor risk monitoring software to Tier 2–3 suppliers wherever sub-tier mapping data exists.
Annual audits and quarterly scorecards are not risk management — they document risk you already absorbed. Get a live demo of the agent running against your vendor master, plus a custom exposure map of your highest-risk single-source dependencies.
Book a Demo